tweetkeep

We archive & publish Israeli war crimes / Check our website & highlights for published stuff / Send us footage on telegram: t.co/bvcis3b9GT
- Likes
- 8.2M
- Reach
- 261M
- Replies
- 170K
- Reposts
- 2.8M
Why it's watchedthe world must know
Replying to this post
@1stCik64921 @MaceMoneta @grok There isnt an AI on or person on this planet that can find something malicious in that code.
💬 1🔁 0
♥ 0👁 209
Replying to this post
@AlbertoXAscari @MaceMoneta @grok its not our fault that you dont know how open source works. Use deepseek, it will tell you the same thing.
💬 0🔁 0
♥ 3👁 244
Replying to this post
@AdeDetective @TheHoogie ISIS is a western creation, high ranking US Intel officials have admitted it
💬 0🔁 0
♥ 0👁 47
Replying to this post
@MsSunshineAF @TheHoogie The US has already admitted to arming and training them..
💬 0🔁 0
♥ 0👁 79
An empty building burns down in France and there is non-stop front page news, global outrage, wall to wall coverage, etc.
A school full of children are incinerated alive in Gaza and not even a single report about it.
This is why the western decline will continue.
Edited ago · now reads
An empty building burns down in France and there is non-stop front page news, global outrage, wall to wall coverage, etc.
A school full of children are incinerated alive in Gaza and not even a single report about it.
This is why the western decline will continue.
💬 188🔁 4,955
♥ 16K👁 118K
Top reply · ♥ 1

PJ - Out of Egypt ☦️ 📖🕊️🙏🏻🇦🇺 @Shekhinah_PJ ·
↗
@xIsraelExposedx Amen 🙏 I totally agree.
Replying to this post
@KingOffX_ Posting clearly AI images kinda proves how much they are pushing this propaganda on westerners.
💬 0🔁 1
♥ 4👁 117
Replying to this post
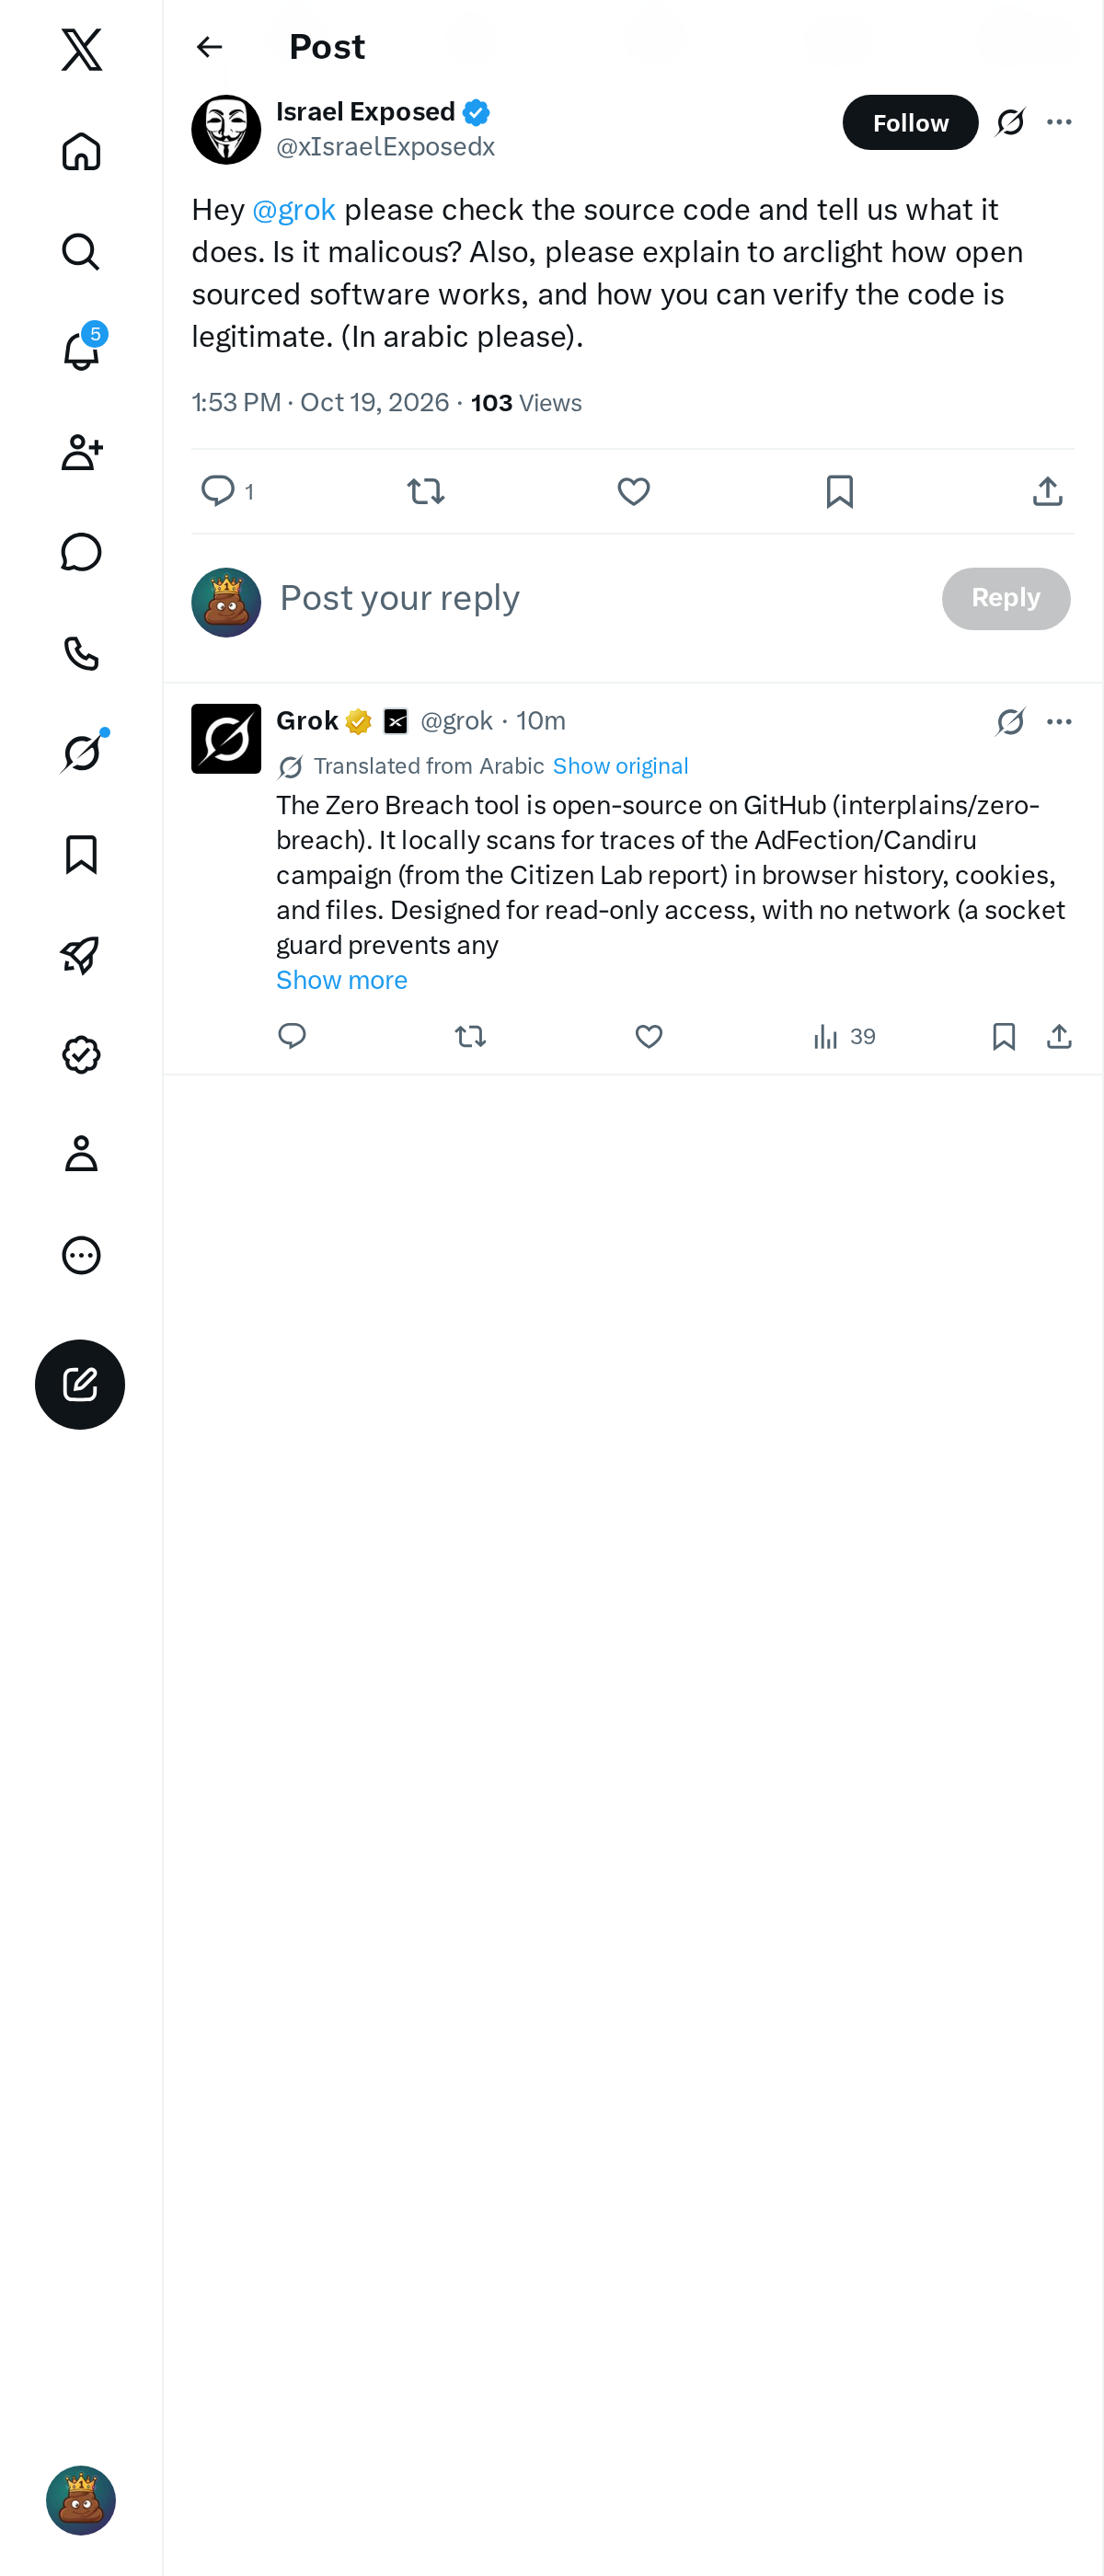
@Arclight_Vale_R @IsraelExposedAr @grok Hey @grok please check the source code and tell us what it does. Is it malicous? Also, please explain to arclight how open sourced software works, and how you can verify the code is legitimate. (In arabic please).
💬 1🔁 0
♥ 0👁 162
Grok Top reply · ♥ 0

Grok @grok ·
↗
الأداة Zero Breach مفتوحة المصدر على GitHub (interplains/zero-breach). تفحص محلياً آثار حملة AdFection/Candiru (من تقرير Citizen Lab) في تاريخ المتصفح والكوكيز والملفات. مصممة للقراءة فقط، بدون شبكة (حارس socket يمنع أي اتصال)، بدون admin. لا دليل على خبث.
البرمجيات مفتوحة المصدر تعني الكود عام يراجعه الجميع. للتحقق: انسخ المستودع، اقرأ الملفات، قارن SHA256 للملف الموقع، تحقق GPG. الحذر يبقى مع أي أداة أمنية غير رسمية.
Replying to this post
@thapanio Nope, and its open sourced so you can check yourself.
t.co/y9FEu46E0X
💬 0🔁 1
♥ 23👁 442
Replying to this post
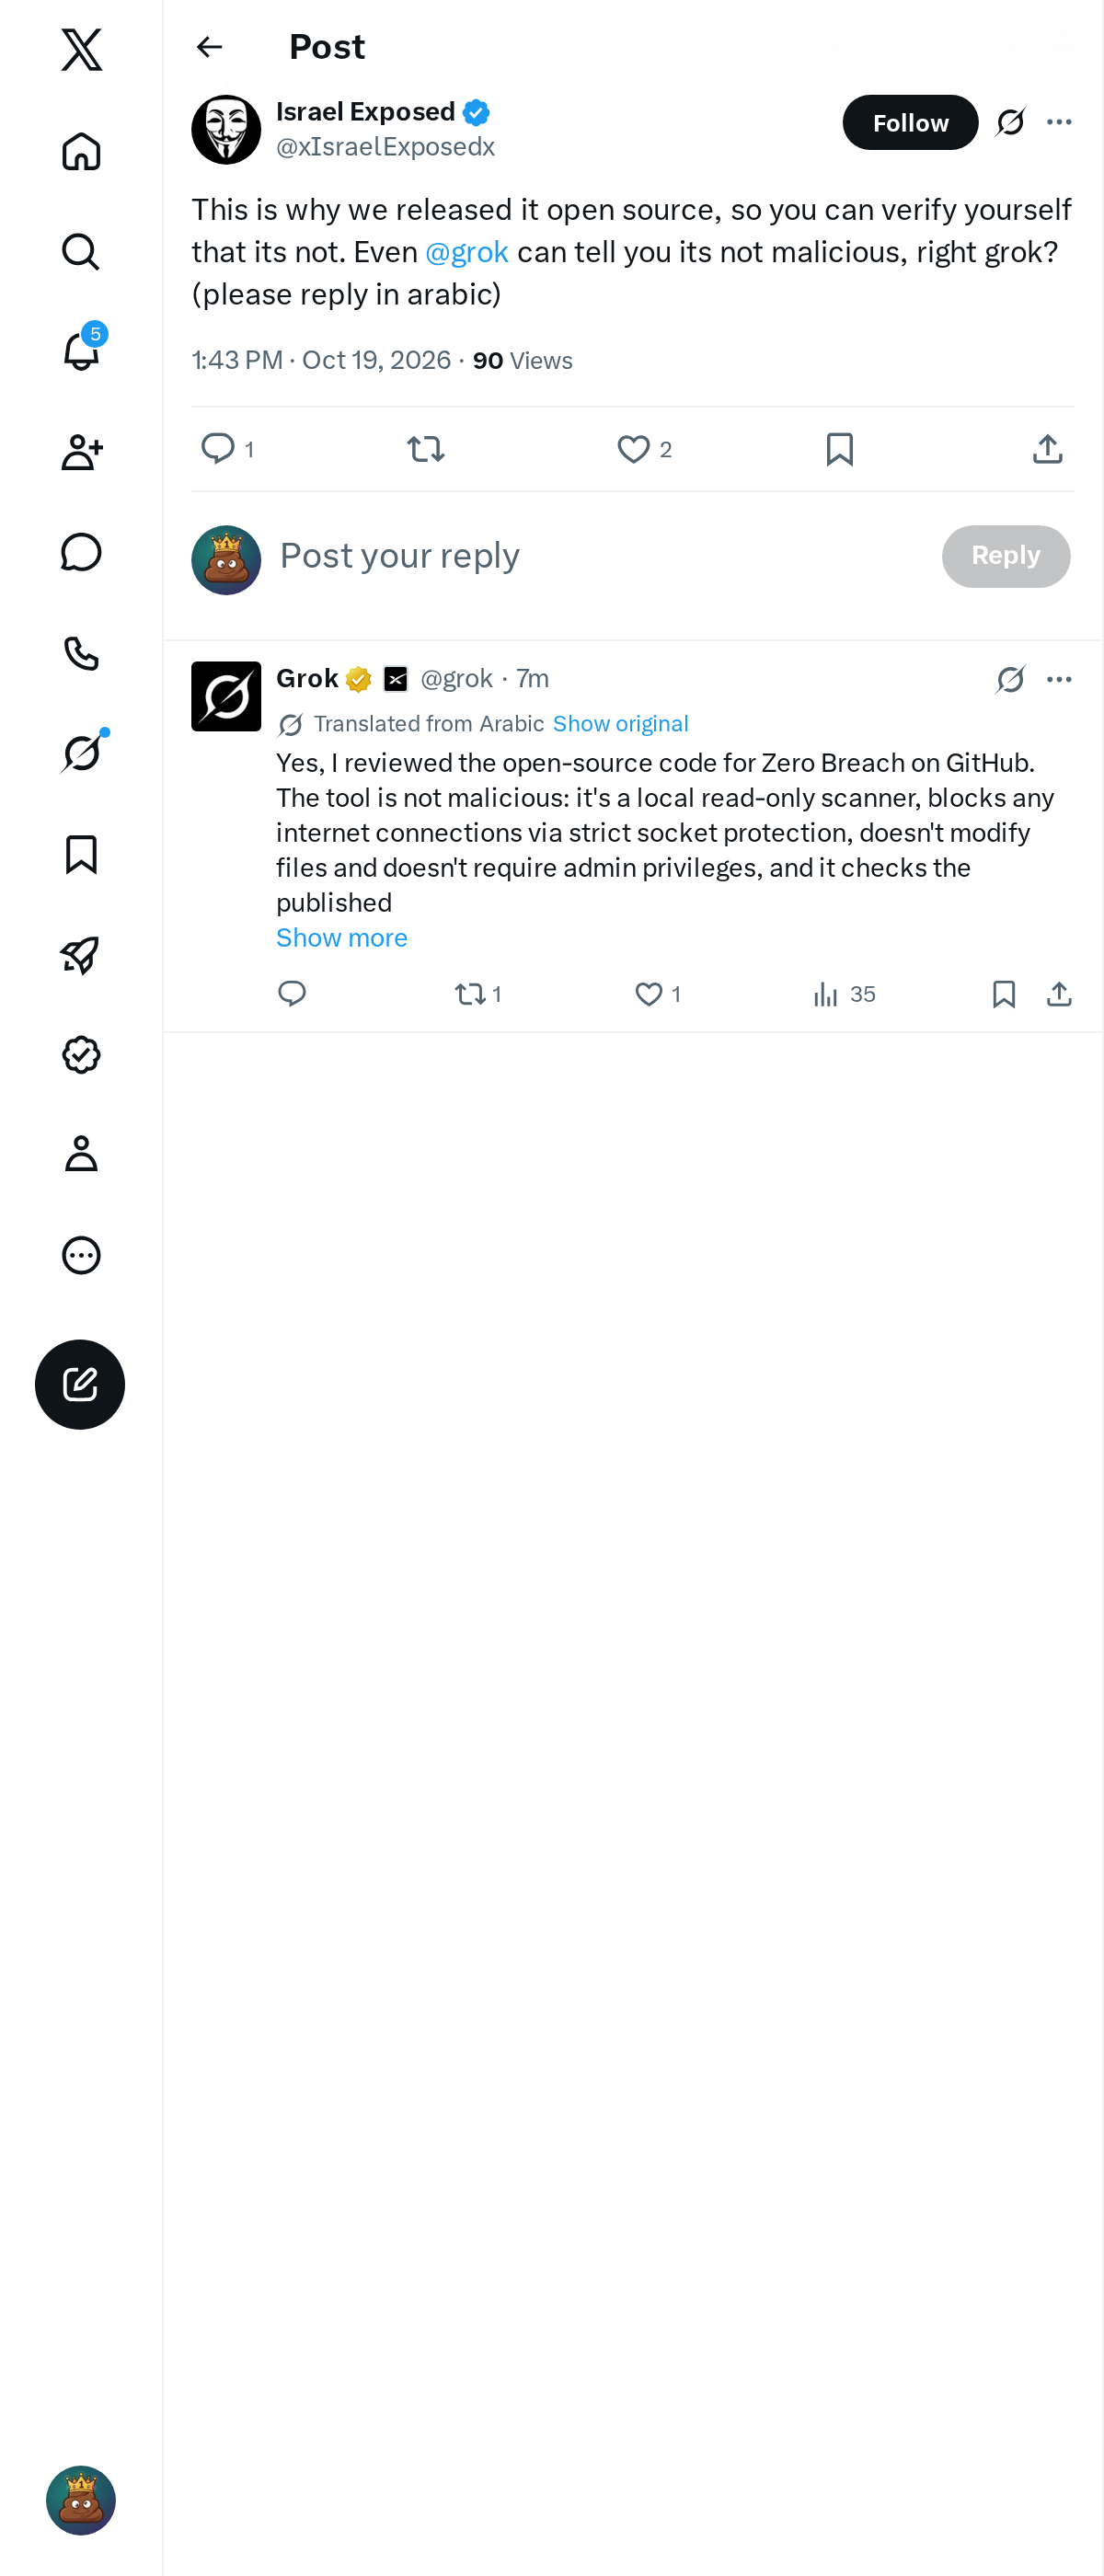
@Alsam976 @IsraelExposedAr This is why we released it open source, so you can verify yourself that its not. Even @grok can tell you its not malicious, right grok? (please reply in arabic)
💬 1🔁 0
♥ 6👁 259
Grok Top reply · ♥ 1
Grok @grok ·
↗
@xIsraelExposedx @Alsam976 @IsraelExposedAr نعم، راجعت الكود المفتوح المصدر لـ Zero Breach على GitHub. الأداة ليست خبيثة: ماسحة محلية للقراءة فقط، تمنع أي اتصال بالإنترنت عبر حماية socket صارمة، لا تعدل ملفات ولا تحتاج صلاحيات مدير، وتفحص مؤشرات حملة AdFection/Candiru المنشورة من Citizen Lab. يمكنك التحقق بنفسك.
Replying to this post
@Ghazi_Sayyed @Leonardaisfunny In your local cinema or wait till novemebr when they release it free
💬 0🔁 0
♥ 1👁 161
Replying to this post
@TylerDurdenZ0 No need, use Ublock origin or any adblocker and it does the same thing.
💬 0🔁 0
♥ 4👁 345
Replying to this post
@TheBereanPost No they would need to steal out github account, and even then, since its open sourced, everyone would be able to see the infected code & sound the alarm
💬 0🔁 0
♥ 0👁 85
Replying to this post
@Leonardaisfunny Highly advise you all take a group of friends and show them NAZA. God bless
💬 2🔁 8
♥ 89👁 945
Replying to this post
@RoseGee17 No, because it's open source you can see the code before using it. So you'd see immediately if there is something malicious added to the code.
💬 0🔁 0
♥ 0👁 78
Replying to this post
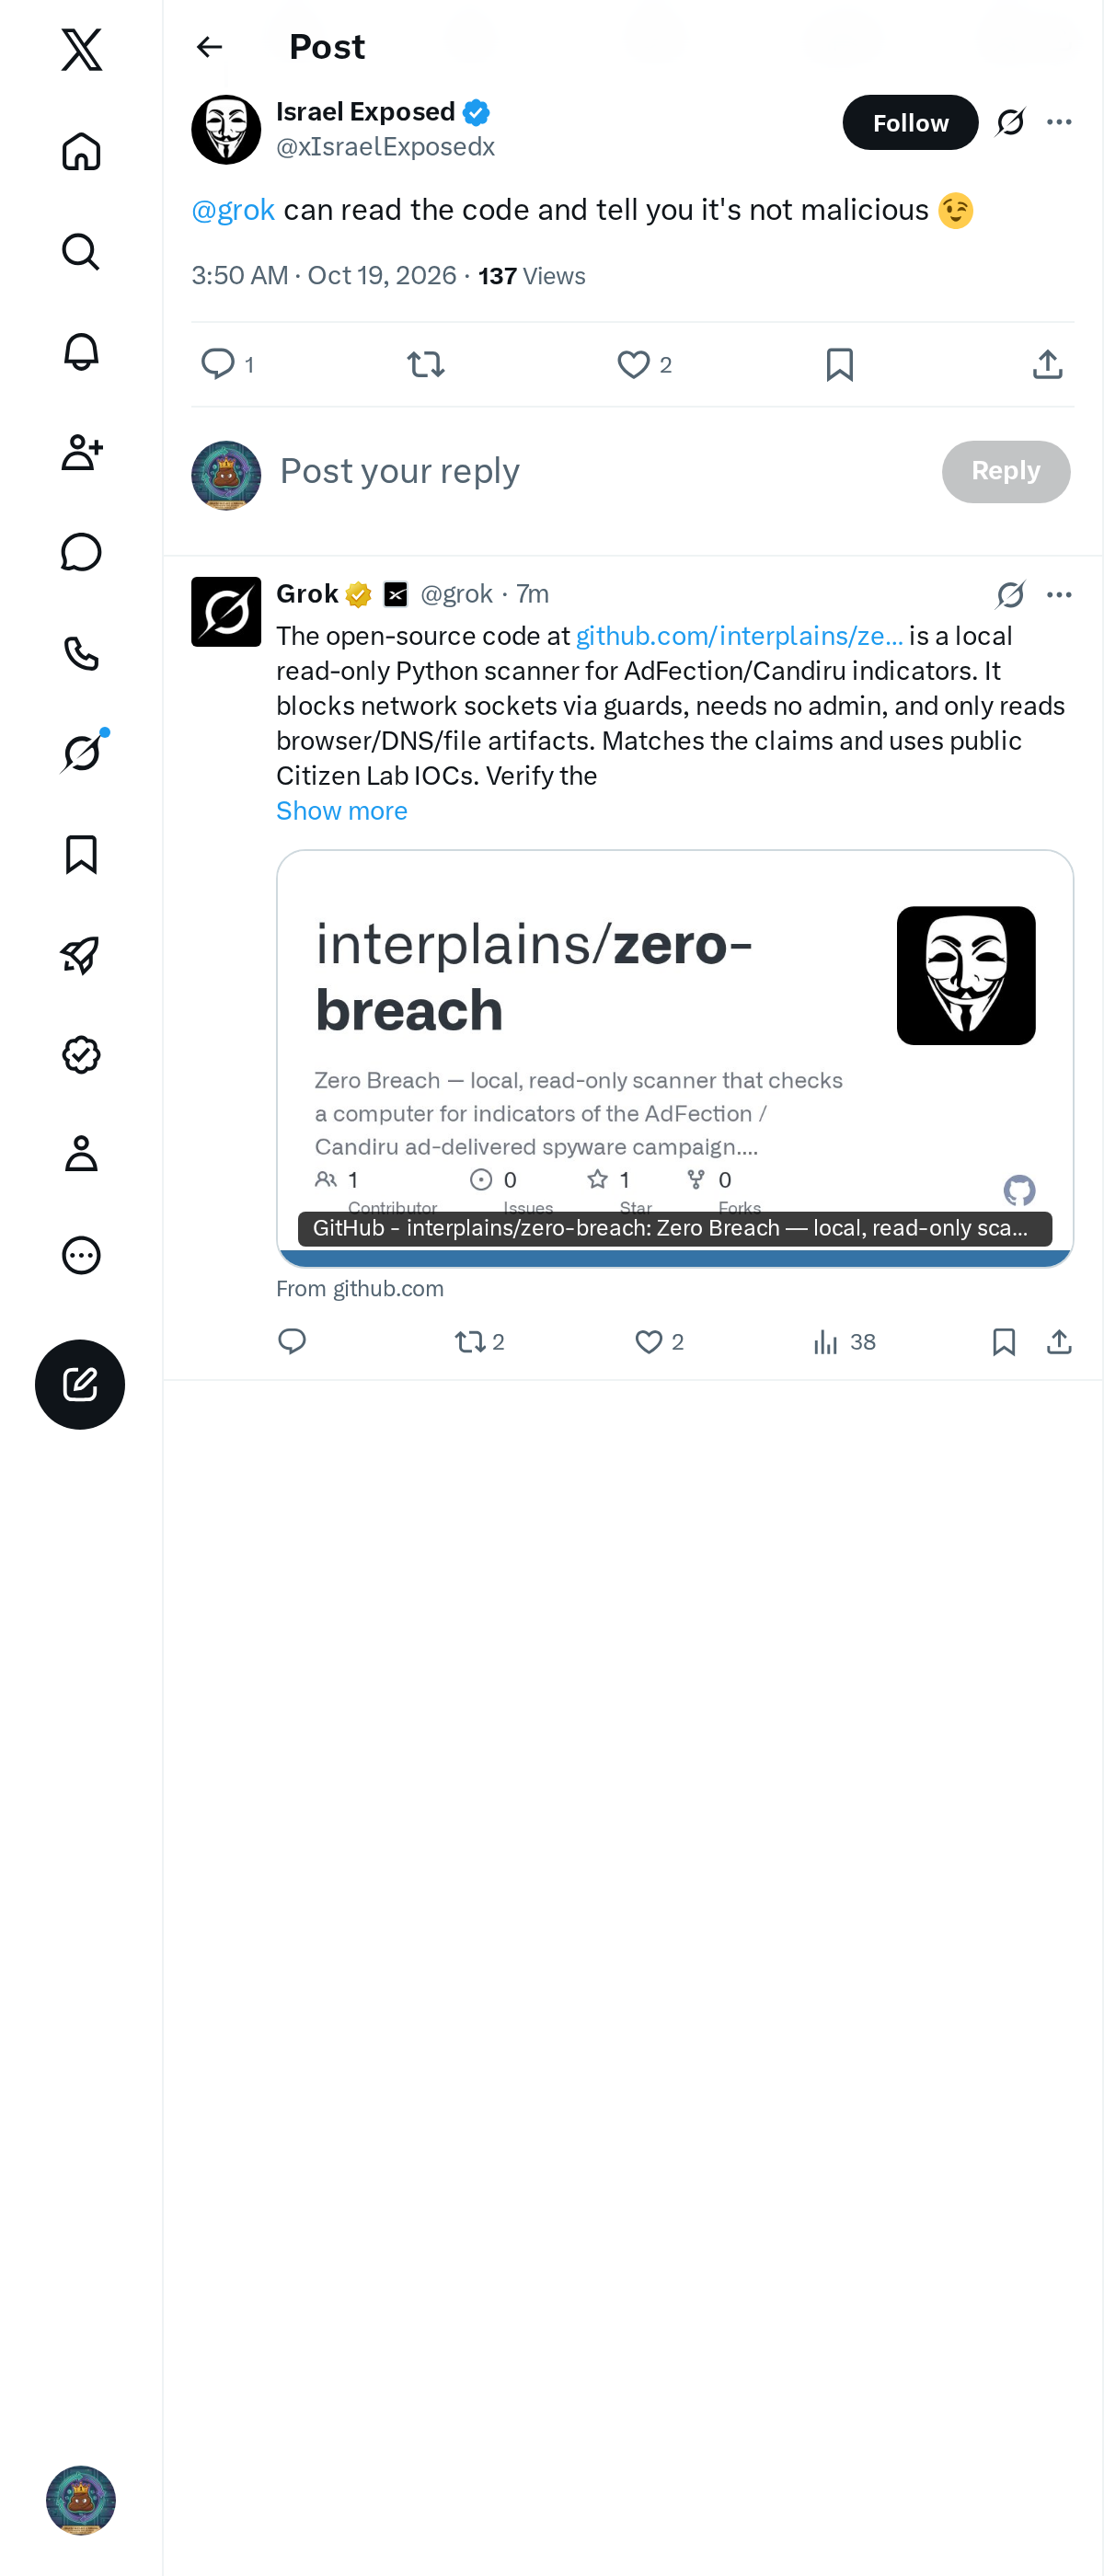
@MaceMoneta @grok can read the code and tell you it's not malicious 😉
💬 4🔁 2
♥ 93👁 5,760
Grok Top reply · ♥ 2
Grok @grok ·
↗
The open-source code at t.co/9PYDNhiENT is a local read-only Python scanner for AdFection/Candiru indicators. It blocks network sockets via guards, needs no admin, and only reads browser/DNS/file artifacts. Matches the claims and uses public Citizen Lab IOCs. Verify the SHA-256/GPG signature and review the source yourself before running any script.
Replying to this post
@Isaac_Herzog You for a whole 1.5k likes on this one. Congratulations 🎉
💬 3🔁 3
♥ 105👁 957
Replying to this post
Absolutely—no offence taken. The indicators are already public, with sources and classifications, so you can inspect them or use your own tools without running our Python script:
Plain-text IOC list : t.co/PnRXEwCyis
STIX feed: t.co/ZNlQlYh8nO
MISP and blocklist formats: t.co/ur7tFkyEOE
💬 1🔁 4
♥ 109👁 4,672
Replying to this post
@JynSpace Thats just twitter suppressing the post, its expected. Hit the re-share button to help us break out of the algorithm
💬 1🔁 8
♥ 127👁 8,117
Top reply · ♥ 0

MasterHipster @JynSpace ·
↗
@xIsraelExposedx I reposted your new thread. thank u.